Understand visitorsSee why they don’t buy
Website Heatmap ToolClicks, scroll depth and attention on every pageSession Replay SoftwareWatch real visits and see where people get stuckError Tracking ToolNEWJS, 404 and 5xx errors that break the checkoutMeasure revenueKnow which pages and ads make money
Traffic ValueNEWWhich landing pages and channels lose you salesEcommerce AnalyticsRevenue, orders and AOV by channel, product and page blockWebsite Funnel AnalysisThe exact step where visitors drop offEvent Tracking ToolsTrack clicks and goals without code, send to GA4Convert & testFix the leak and prove it worked
Pop-Up SoftwareTargeted pop-ups that capture leads and salesWebsite Feedback ToolAsk visitors why they didn’t buyA/B Testing ToolFreeTest a change on live traffic and pick the winnerGrow search trafficSEO monitoring and competitors
SEO CheckerDaily site audit and Search Console alertsSERP CheckerAdd-onCompare your page with Google’s top 10Free Chrome extensionsCheck any website in one click
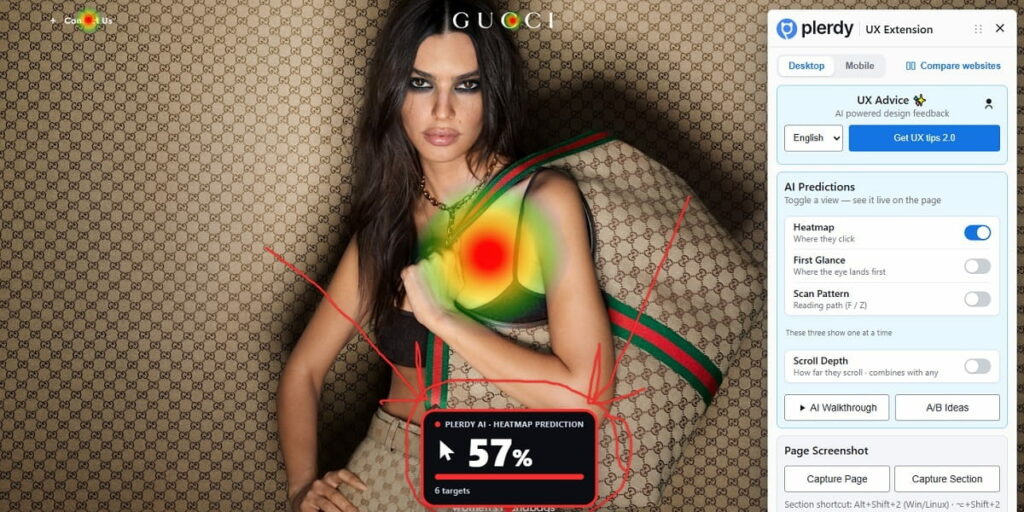
Chrome SEO AnalyzerOn-page SEO check of any site in one clickChrome UX AnalyzerAI-predicted attention heatmap, no code neededAll tools in one planInstead of five separate subscriptions
Quick setupShopify, WordPress, Wix or one script
Works with Claude & ChatGPTAsk your data in plain words
Understand visitorsSee why they don’t buy
Website Heatmap ToolClicks, scroll depth and attention on every pageSession Replay SoftwareWatch real visits and see where people get stuckError Tracking ToolNEWJS, 404 and 5xx errors that break the checkoutMeasure revenueKnow which pages and ads make money
Traffic ValueNEWWhich landing pages and channels lose you salesEcommerce AnalyticsRevenue, orders and AOV by channel, product and page blockWebsite Funnel AnalysisThe exact step where visitors drop offEvent Tracking ToolsTrack clicks and goals without code, send to GA4Convert & testFix the leak and prove it worked
Pop-Up SoftwareTargeted pop-ups that capture leads and salesWebsite Feedback ToolAsk visitors why they didn’t buyA/B Testing ToolFreeTest a change on live traffic and pick the winnerGrow search trafficSEO monitoring and competitors
SEO CheckerDaily site audit and Search Console alertsSERP CheckerAdd-onCompare your page with Google’s top 10Free Chrome extensionsCheck any website in one click
Chrome SEO AnalyzerOn-page SEO check of any site in one clickChrome UX AnalyzerAI-predicted attention heatmap, no code neededBlog categoriesAll Articles
Digital marketingContent MarketingEcommerceBusinessSEOWeb DesignToolsEBooksAnalyticsGuideInstallation GuideCasesOn-page SEONewsUser Experience (UX)
Useful links
Website Checklists HubUX GameFree toolsMarketing GlossaryGoogle Analytics 4 CourseAffiliate ProgramPlerdy UX StatisticsChrome extensions
Plerdy SEO AnalyzerFreeChrome extension for instant on-page SEO auditing of any website.Add to Chrome Plerdy UX & Usability TestingFreeChrome extension to improve site design with heatmaps, scroll tracking, and screenshots.Add to Chrome